Open-source recovery gate for coding agents
Prove your recovery works.
Then make the change.
Before your coding agent changes a guarded database, require a tested way back. One command wires the gate into the agent as a hook and an MCP server; every decision and its evidence land in a local ledger.
Latest release: v0.11.4 · MIT · Offline · No account · Linux & macOS
$ restoregap agent install claudeHook and MCP server registered.
agent → Bash: rm /srv/app.dbDENY No fresh recovery proof. Run: restoregap drill
$ restoregap drillRESTORED Recovered data passed its checks.
agent → Bash: rm /srv/app.dbALLOW Required recovery proof is fresh.
proposed: delete_file /srv/app.dbevidence: recovery drill passed · proof fresh
$ restoregap ledger showThe gate answers in the agent's own decision format; it does not execute the change.
You know the drill.
A backup job succeeded.
Could you actually recover?
Restore Gap works with the backups you already have. It checks the recovery path, records what a real drill proved, and puts that evidence in front of your next risky change.
check
Compare a live directory with its recovery copy. Find missing files and differences, including which copy is newer.
drill
Run a configured restore in a temporary workspace. Validate recovered bytes, data, or a started service. Record the result and its expiry.
preflight
Match a declared change to your guards. Refuse it when required evidence is missing, failed, or too old.
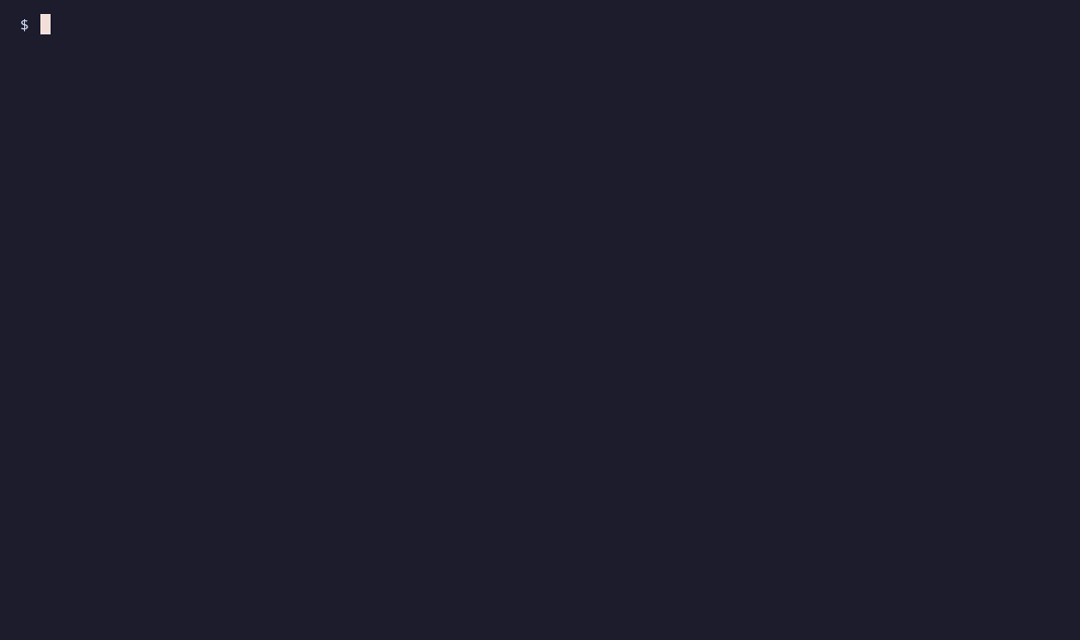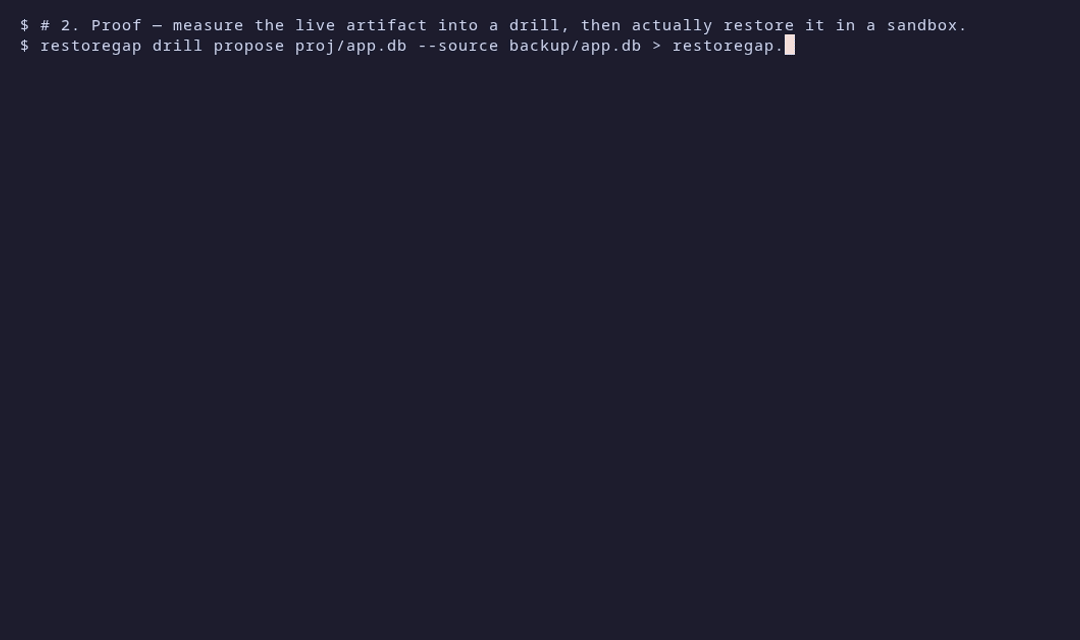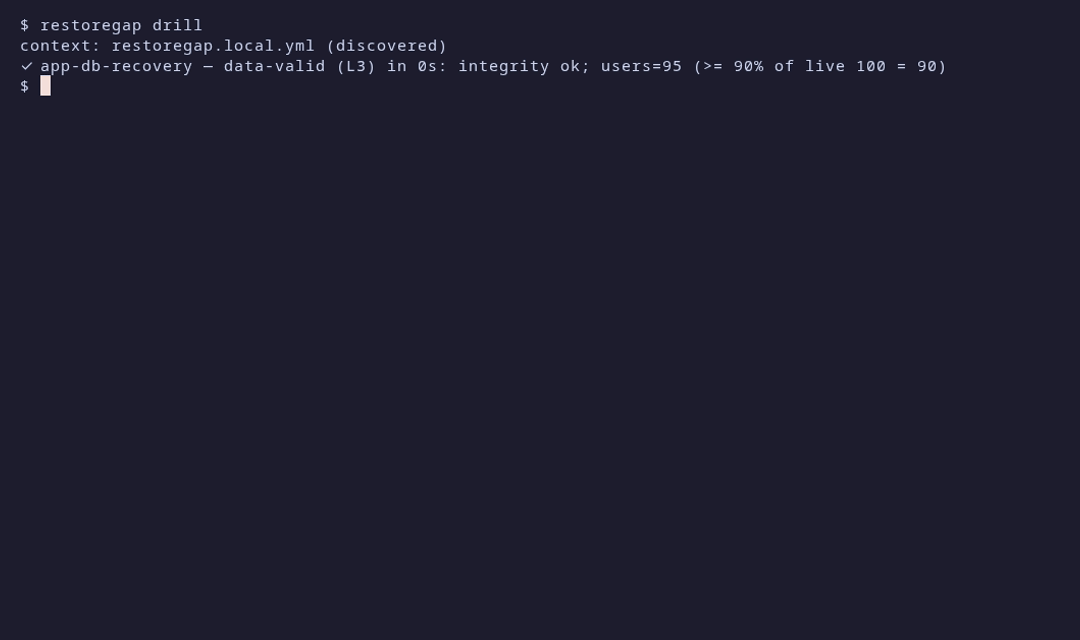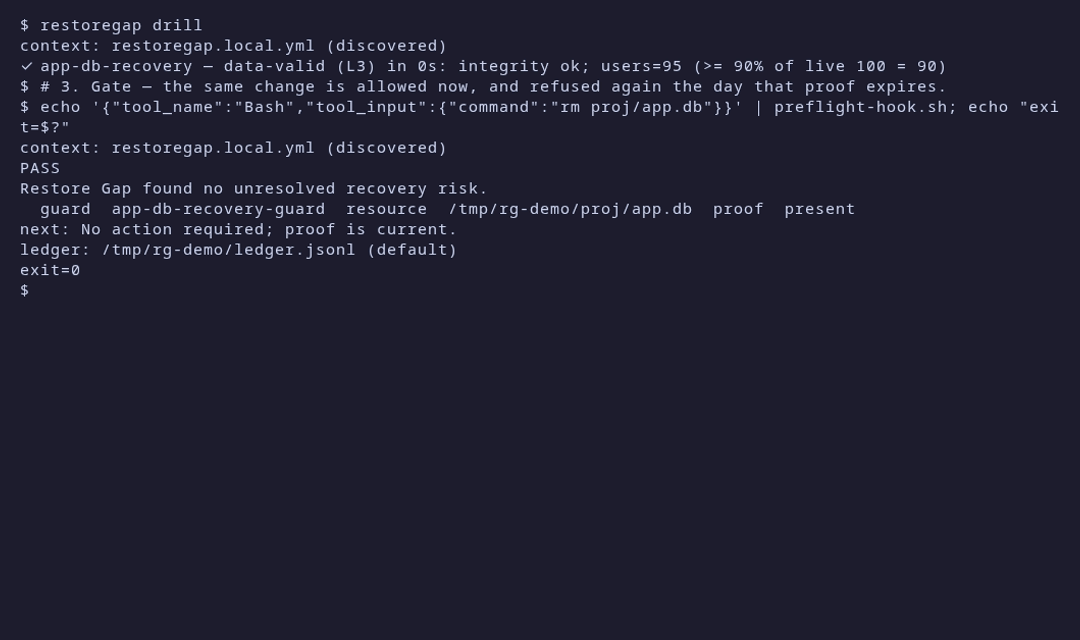
Your first drill, on disposable data.
Install the binary, download the example, and watch the same intent block, pass, then block again when the proof expires.
1. Install
curl -sSfLO https://raw.githubusercontent.com/tannernicol/restoregap/v0.11.4/scripts/install.sh
less install.sh
RESTOREGAP_VERSION=v0.11.4 sh install.sh
export PATH="$HOME/.local/bin:$PATH"
2. Run the example
git clone --depth 1 --branch v0.11.4 https://github.com/tannernicol/restoregap.git
cd restoregap
bash demo/run.sh
The example needs Bash, Git and SQLite's sqlite3 command. It uses disposable files and a separate ledger. You do not need to give it your backups.
For Claude Code, Gemini CLI, scripts and CI
Put the proof before the permission.
restoregap agent install claude registers the pre-tool hook and the MCP server. The hook covers documented command shapes and file edits; the MCP tools and the CLI expose the same recovery decision for anything else.
Know what the gate proves.
Only declared guards and configured integrations are covered. This is not a universal shell interceptor.
A drill's claim is limited to the restore and checks you authored. Its temporary workspace is not an operating-system security sandbox.
A fresh proof records a successful test. It cannot guarantee a future recovery under every failure.
The whole local tool stays free.
Paying should buy an operated service—not unlock a recovery check you need.
Run it yourself
- Check, drill, gate, ledger and agent integrations
- Local proof history; proofs may be signed
- Offline verification and multi-host fleet views
- No account or service dependency
Evidence that stays off-host
- Retained history from explicitly enrolled machines
- Alerts when expected proof fails, expires, or stops arriving
- Private verification links and portable exports
- You keep ownership of your backups and recovery
Include your host count and the problem you would pay to stop managing. This is an interest check, not a checkout.
Before you trust it.
Is this another backup tool?
No. It runs and validates a recovery procedure using your existing copies and tools. It neither replaces their storage nor fixes missing backups for you.
What happens when a proof expires?
A matching guard requiring fresh proof can block the next change. Run the drill again, change the plan, or record an explicit owner override. An override is not a successful restore.
Does a signed proof mean independently certified recovery?
No. Signing establishes record provenance. The claim still depends on the recovery procedure, checks, and environment that produced the evidence.
How much real-world use has it had?
It is used on the author's own machines. That is dogfooding, not independent customer validation. The walkthrough uses synthetic data; no live household data is included.